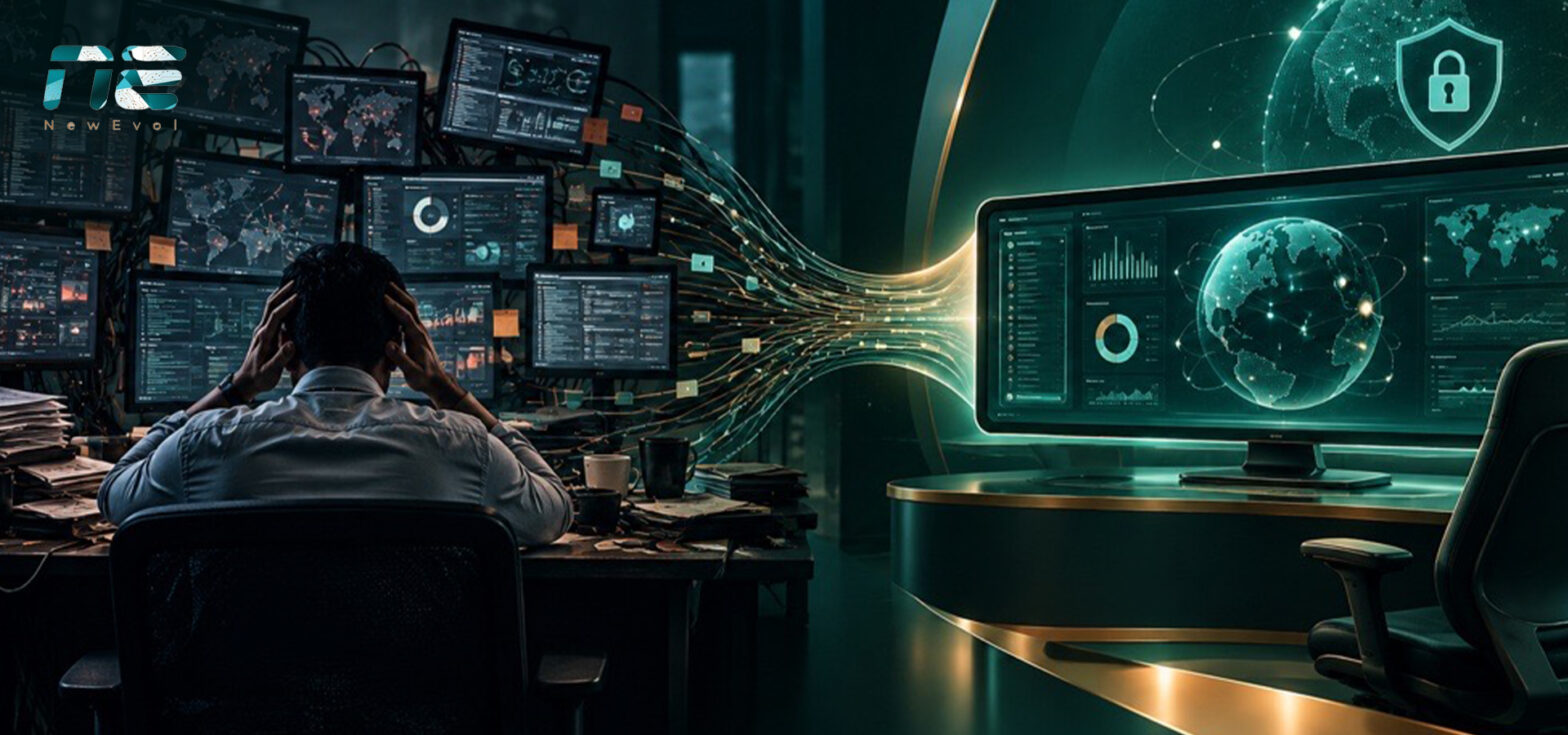
Most conversations about security tool sprawl start with a licence renewal spreadsheet. Someone counts the tools, adds up the annual spend, and asks whether the organisation really needs all of them.
That is a fair question, but it measures the wrong thing. The bigger operational cost of running many security consoles is rarely the invoice. It is the time analysts spend assembling enough information to understand a single alert.
This article calls that cost time to context. It is measurable, it compounds quietly across thousands of alerts, and most security teams have never put a number against it. Below is a practical way to measure it in your own environment before your next renewal or platform expansion.
What Is Security Tool Sprawl?
Security tool sprawl is what happens when an organisation accumulates so many separate security products that the work of moving between them becomes a job in itself.
It is almost never the result of a bad decision. It is the result of many reasonable ones, made over several years:
- A SIEM (Security Information and Event Management platform) is bought to centralise logs.
- An EDR (Endpoint Detection and Response) tool is added after a ransomware scare.
- NDR (Network Detection and Response) arrives to cover traffic the endpoint agent cannot see.
- A SOAR (Security Orchestration, Automation and Response) platform is layered on to automate repetitive tasks.
- Threat intelligence, cloud security posture management, identity monitoring and vulnerability management each get their own console.
Every one of those tools can be justified on its own. The problem is that nobody ever designs the workflow that runs across all of them. Analysts are left to stitch the tools together manually, alert by alert.
The Real Cost: Time to Context
Context is everything an analyst needs before making a decision about an alert. Who is the user? Is the device managed? Has this IP appeared before? Did anything else happen on that host in the same hour?
Time to context is simply the elapsed time between an alert arriving and an analyst having enough of that information to act on it.
In a fragmented environment, that time is consumed by work that produces no security value on its own:
- Searching for the same host or user in three or four separate consoles.
- Switching between browser tabs and re-orienting to a different interface each time.
- Re-authenticating, or waiting for a session to load.
- Copying an indicator out of one platform and pasting it into another.
- Manually lining up timestamps across tools that use different time formats.
- Repeating the same enrichment steps for the fifth similar alert that shift.
None of these steps is expensive by itself. Ninety seconds here, two minutes there. The cost only becomes visible when you multiply it by alert volume. A SOC handling 300 alerts a day at four extra minutes of pivoting per alert is spending roughly 20 analyst hours a day on navigation rather than analysis.
Where Tool Sprawl Slows Down SOC Analysts
Pivot Cost During Live Incidents
Consider a realistic sequence. An alert fires in the SIEM for suspicious PowerShell activity on a finance workstation.
- The analyst opens the EDR console to see the full process tree and whether the binary executed.
- Identity context comes from a separate directory or IAM tool: is this a privileged account, and did the user travel recently?
- Network telemetry lives in the NDR platform, which shows whether the host contacted an external address afterwards.
- The destination IP is checked against a threat intelligence portal.
- Vulnerability data is pulled from another system to see whether the host was already exposed.
That is five consoles for one alert. Each pivot adds time, and each one is a chance to lose the thread. An analyst who finds nothing useful in step three may reasonably stop before reaching step five, which is where the confirming evidence happened to be.
Inconsistent Enrichment
Different platforms enrich the same alert differently. The EDR might rate an IP as low risk while the threat intelligence feed flags it as suspicious. Asset criticality may be recorded in the CMDB but missing from the SIEM. Severity scoring rarely matches across vendors.
The practical effect is that two analysts investigating similar alerts can end up with different pictures of the same event, depending on which tools they opened and in which order. Investigations become less predictable and harder to review afterwards.
Detection Logic Duplication and Drift
When detection capability exists in several platforms, similar logic tends to get written in each of them. A rule for impossible travel might live in the SIEM, the identity platform and the cloud security tool at the same time.
Over time these copies drift apart. A threshold is tuned in one place and not the others. A rule is retired in the SIEM but keeps firing elsewhere. Maintenance effort grows, and confidence in any single detection falls.
This is not automatically an argument for removing tools. It is an argument for knowing how many duplicated rules you actually maintain.
Shift Handover Gaps
Investigation notes tend to be written wherever the analyst happened to be working. Some sit in the SIEM case, some in the EDR, some in a ticketing system, some in a chat thread.
The incoming shift then reconstructs the investigation rather than continuing it. Searches get repeated, and the reasoning behind an earlier decision is often lost. Handover time is one of the easiest tool sprawl costs to measure, because someone can simply time it for a fortnight.
Tab Management and Analyst Fatigue
Ask analysts what wears them down and tab management comes up surprisingly often. Twenty open tabs, repeated logins, the same three enrichment lookups for the fortieth time that week.
Tool sprawl is not the sole cause of SOC attrition, and it would be misleading to claim otherwise. Shift patterns, alert volume, career progression and pay all matter more. But repetitive operational friction is one factor worth monitoring, because it steadily reduces the share of the day spent on work analysts find meaningful.
How to Measure Tool Sprawl Before Your Next Renewal
Rather than assuming more tools equals more inefficiency, collect two weeks of baseline data. Nine metrics are enough:
- Consoles touched per incident
- Average time to gather context
- Manual pivots per investigation
- Enrichment steps per alert
- Repeated searches per alert
- Time spent switching between tools
- Duplicated or overlapping detection rules
- Time required for shift handover
- Percentage of investigations needing data from more than one platform
A simple calculation. Suppose a team of six analysts handles 250 alerts per day, and measurement shows an average of 3.5 minutes per alert spent purely on navigation and manual enrichment. That is roughly 875 minutes daily, close to 15 analyst hours, or about 2.7 full-time equivalents each week. Even halving it is a meaningful gain, and it is a figure you can take into a renewal conversation.
A Practical SOC Tool-Sprawl Scorecard
|
Metric |
Target |
Potential operational impact |
|
Consoles touched per incident |
2 or fewer |
Fewer pivots, faster triage |
|
Average time to gather context |
Under 5 minutes |
Shorter investigation cycles |
|
Manual pivots per investigation |
3 or fewer |
Less chance of missed evidence |
|
Enrichment steps performed manually |
Mostly automated |
More consistent conclusions |
|
Repeated searches per alert |
Near zero |
Reduced duplicated effort |
|
Duplicated detection rules |
Documented and owned |
Lower maintenance burden |
|
Shift handover duration |
Under 15 minutes |
Continuity between shifts |
|
Investigations needing multiple platforms |
Tracked monthly |
Shows where integration pays off |
Fill the current column with real observations, not estimates. The gaps will point to the friction worth fixing.
Does Every SOC Need Consolidation?
No, and it is worth saying so plainly. Best-of-breed architectures exist for good reasons:
- Specialist tools genuinely outperform generalist modules in some areas, particularly cloud workload and OT security.
- Regulatory or sector requirements sometimes mandate specific controls or deployment models.
- Existing multi-year investments may still have useful life.
- Hybrid, multi-cloud and OT environments rarely fit one platform.
- Integration maturity varies, and a consolidated tool with weak connectors can create new blind spots.
The objective is not necessarily fewer tools. It is less unnecessary investigative friction and faster access to context. Those are different goals, and consolidation is only one route to the second.
Where a Single-Console Approach Can Help
A single console SIEM approach aims to bring detection, enrichment and investigation workflow into one working surface, whether the underlying data comes from one platform or several integrated ones.
Where it tends to help:
- Context arrives with the alert rather than being fetched.
- Fewer manual pivots during live incidents.
- Enrichment applied consistently, so two analysts see the same picture.
- Case notes and timelines held in one place, improving handovers.
- Repetitive lookups handled by automation rather than by people.
It will not eliminate other tools, and no platform guarantees faster detection. Platforms such as NewEvol are best understood as a way to centralise investigation context and workflow, not as a replacement for a well-designed operating model.
How to Start Measuring Your Environment
Pick ten recent investigations. For each, record the consoles opened, the pivots made and the total time to reach a decision. Time three shift handovers. Export detection rules from each platform and look for overlaps. Two weeks of this will tell you more than any vendor comparison.
Conclusion
Tool sprawl is an operational cost before it is a financial one, and it shows up as time to context. Measure that number in your own SOC first. Then decide whether consolidation, better integration, or a deliberate best-of-breed approach makes the most sense for your environment. The evidence should come before the architecture decision, not after it.
Frequently Asked Questions
1. What is security tool sprawl in a SOC?
It is the accumulation of many separate security products, each with its own console, to the point where moving between them consumes a significant share of analyst time during alert investigation.
2. How many security tools is too many?
There is no fixed number. A useful indicator is consoles touched per incident. If routine investigations regularly require four or more platforms, the workflow is worth reviewing.
3. What does “time to context” mean?
It is the time between an alert arriving and an analyst having enough information, such as user, asset, network and threat intelligence detail, to decide what to do next.
4. Does a single console SIEM replace EDR, NDR and SOAR?
Generally no. It is more accurate to think of it as unifying the investigation surface and the workflow, while specialist tools continue to supply telemetry and enforcement.
5. Is consolidating security tools always cheaper?
Not necessarily. Licence savings can be offset by migration effort, retraining and lost specialist capability. The stronger case is usually operational efficiency, which is why it should be measured first.
6. How do I measure tool sprawl before a renewal?
Track consoles per incident, manual pivots, enrichment steps, repeated searches, duplicated detection rules and handover duration over two weeks, then multiply the per-alert overhead by your alert volume.
7. Does tool sprawl cause SOC analyst attrition?
It is one contributing factor rather than the cause. Repetitive navigation and fragmented context reduce time spent on meaningful analysis, which matters alongside shift patterns, workload and progression.