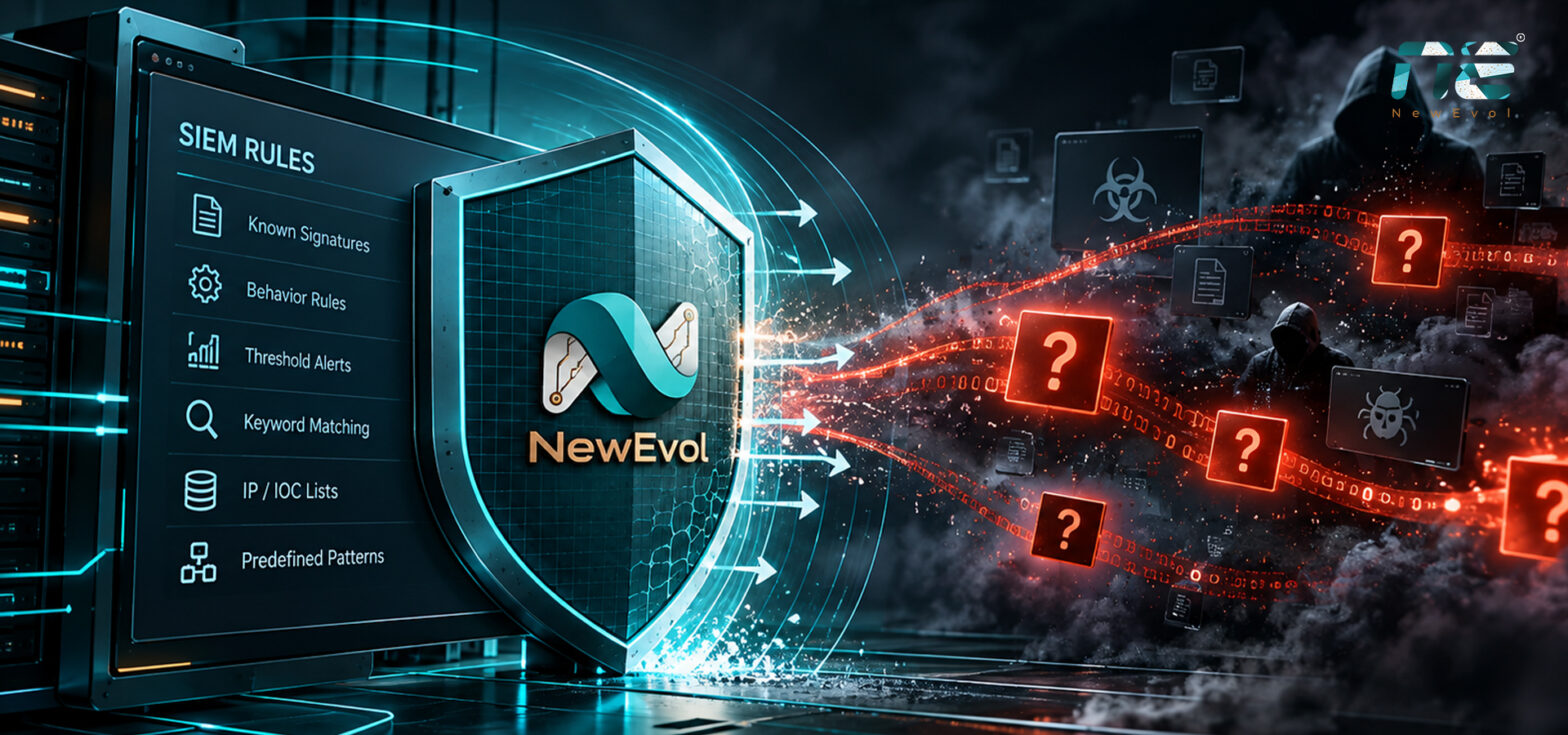
An attacker signs in with a valid account. Using PowerShell and a remote management tool already approved on the network, they explore file servers and copy data out in small batches. The SIEM collects every log. The login succeeded, the tools are legitimate, and no single transfer crosses a threshold. No rule fires.
The SIEM did not fail here. The logs were there. What was missing was detection logic that described this particular combination of actions. Collecting security data does not guarantee that every meaningful threat will be detected.
That gap sits at the heart of rule-based SIEM limitations. A detection rule encodes a threat that someone already understood. When attackers introduce a new technique or change their behaviour, existing rules may not recognize it. A sound detection strategy therefore needs to cover both known attack patterns and suspicious behaviour that has not yet been documented.
How Rule-Based SIEM Detection Works
A security information and event management (SIEM) platform collects logs from endpoints, servers, network devices, cloud services and applications, then evaluates them against SIEM detection rules. A rule is a predefined condition: if certain events occur, in a certain pattern, within a certain window, raise an alert.
Rules typically handle:
- Matching log events against known detection logic
- Spotting repeated failed logins or unusual authentication patterns
- Flagging known malicious indicators such as file hashes, domains or IP addresses
- Correlating several related events into one higher-priority alert
- Producing consistent alerts that analysts can explain and reproduce
A simple example: alert when one account records ten failed logins within five minutes. Against an attacker guessing a password, that rule works reliably.
This approach is effective when the rule accurately describes the activity it targets and the data it needs actually reaches the SIEM.
Why Known Detection Rules Miss New and Unknown Threats
Rules are written from experience. That is their strength and their boundary. Six factors explain most threat detection gaps.
- New attack techniques. A rule cannot exist for a technique defenders have not yet observed or understood.
- Changes to familiar techniques. Attackers can alter commands, reorder steps or slow their timing. A rule looking for one exact command string may miss the same action written differently.
- Living-off-the-land activity. Administrators use built-in tools such as PowerShell, WMI and remote desktop every day. When attackers misuse them, the activity rarely looks malicious in isolation.
- Unfamiliar event sequences. A login, a file query and an outbound connection may each be normal. Together, in that order, they may point to a compromise.
- Incomplete coverage. A rule cannot catch what its logic does not describe or what the telemetry does not record. If endpoint process logs are never collected, process-based rules have nothing to evaluate.
- Overly narrow conditions. Exact strings, fixed thresholds and rigid sequences let small variations slip past.
Return to the failed-login rule. It catches a noisy brute-force attempt. Now picture an attacker trying one common password against hundreds of accounts, once each, spread across a day. No account reaches ten failures, so the rule stays silent while working exactly as written.
A missed alert does not necessarily mean the SIEM malfunctioned. The detection logic, the available data or the assumptions behind the rule were simply insufficient for what actually happened.
The Difference Between Rule-Based Detection and Behavioural Analytics
Rule-based detection asks whether activity matches a known condition. Behavioural approaches ask whether activity differs from what is expected. Each answers a different question.
|
Detection approach |
How it works |
Main strength |
Key limitation |
|---|---|---|---|
|
Rule-based detection |
Matches events against predefined conditions |
Consistent detection of known patterns |
May miss activity outside the rule’s logic |
|
Signature-based detection |
Matches recognized malicious indicators or signatures |
Effective for known threats with identifiable indicators |
May not recognize new or modified indicators |
|
Behavioural baselining |
Establishes patterns of normal activity for users, systems or networks |
Helps identify unusual behaviour |
Requires suitable data and reliable baselines |
|
Anomaly detection |
Flags activity that differs from expected patterns or statistical models |
Can highlight previously unrecognized activity |
Unusual does not automatically mean malicious |
|
Correlation and security analytics |
Combines events, context and relationships to identify suspicious patterns |
Provides broader context across multiple events |
Depends on data quality, analytics design and tuning |
These approaches are not interchangeable. They work best together, each covering ground the others cannot.
How Behavioural Baselining Helps Identify Unknown Threats
Behavioural baselining builds a picture of normal activity for users, endpoints, applications and network connections, then compares new activity against it. Useful deviations include:
- A user accessing sensitive systems at 3 a.m. when they normally work office hours
- An account reaching resources it rarely or never uses
- A service account suddenly generating far larger data transfers than usual
- A workstation communicating with systems outside its typical pattern
None of these needs a rule written for the exact sequence of events. The baseline supplies the missing context.
Normal is not one fixed thing, though. It varies between users, departments, business cycles and environments. A finance team at quarter-end behaves differently from the rest of the year. A deviation is a reason to investigate in context, not proof of an attack.
The Role of Anomaly Detection and Security Analytics
Anomaly detection extends baselining with statistical models and correlation. Instead of describing a threat in advance, it highlights activity that departs from established patterns. In practice this means:
- Measuring statistical deviations from typical activity
- Linking related events across different systems
- Prioritizing unusual activity by risk, so the most concerning items surface first
- Correlating authentication, endpoint, network and application telemetry
- Supporting investigation of activity that looks suspicious but is not conclusively malicious
Consider an employee account that authenticates successfully, opens an unfamiliar server and transfers an unusual volume of data. Each event could be legitimate on its own. Combined, they justify a closer look.
Analytics can reveal patterns like this, but results depend on the available data, the detection design, business context and analyst validation. Anomaly detection does not find every unknown attack, and it does not remove the need for human investigation.
The Hidden Cost of Behavioural and Anomaly-Based Detection
Extending detection beyond rules brings real operational costs that teams should plan for:
- False positives: Legitimate changes, such as a new project or a system migration, can look suspicious.
- Tuning effort: Thresholds and behavioural models need ongoing adjustment.
- Data quality: Missing, inconsistent or poorly normalized logs weaken any analysis built on them.
- Baseline maintenance: Roles, operations and infrastructure change, and baselines must keep pace.
- Analyst workload: Too many low-value alerts can overwhelm the people investigating them.
- Operational complexity: Each method needs suitable expertise, testing and governance.
More detection signals do not automatically mean better security outcomes. Effective detection balances coverage, alert quality, investigation capacity and business risk.
Why Traditional SIEM Rules Still Matter
None of this makes rules obsolete. Rule-based detection remains a core part of any effective SIEM environment because it:
- Detects established attack patterns, known indicators and well-understood threats
- Supports compliance and audit requirements
- Applies consistent detection logic across the environment
- Produces explainable alerts with clear triggering conditions
- Enables repeatable testing and supports incident investigation
Rules and analytics also strengthen each other. When behavioural analysis surfaces something unusual, a targeted rule can confirm a specific suspicious condition. When an investigation uncovers a new technique, threat detection engineering can turn that finding into a new rule.
A SIEM’s detection capability depends on its configuration, data sources, analytics and operational practices, not on whether it is labelled traditional. The aim is to strengthen the overall strategy, not to remove rules from it.
How to Evaluate SIEM Detection Coverage Honestly
Whether you are reviewing your current SIEM or assessing a new vendor, these questions test coverage in practical terms:
- Which known attack techniques do existing detection rules cover?
- How are rules tested, maintained and updated?
- What happens when a technique has no existing rule?
- Can the platform identify suspicious behaviour across multiple events and data sources?
- Does it support user and entity behaviour analytics or other anomaly detection methods?
- How are false positives measured and reduced?
- What telemetry does behavioural analytics need to work effectively?
- Can analysts see why an event was flagged as suspicious?
- How is coverage validated through simulations, controlled tests or documented exercises?
- How are gaps identified when an attack scenario fails to trigger an expected alert?
One question deserves particular weight: “If an attack technique has no existing detection rule, how would your platform identify it?”
A strong answer describes the actual detection mechanism, the data it requires, its expected limitations and how it has been validated. A weak answer leans on broad claims about AI or automated threat detection without explaining how detection really works.
Building a More Balanced SIEM Detection Strategy
Improving coverage is a gradual, evidence-driven process:
- Maintain and regularly test rules for known threats.
- Map detection logic to relevant attack techniques, for example using the MITRE ATT&CK framework, and to business risks.
- Improve log collection, normalization and telemetry coverage.
- Introduce behavioural baselines where suitable data is available.
- Use anomaly detection and correlation to find suspicious patterns beyond fixed conditions.
- Review false positives and missed detections, and feed the lessons back into detection logic.
- Test scenarios that deliberately lack a direct, predefined rule.
- Measure detection quality through documented results and continuous improvement.
The same discipline applies when comparing platforms. Teams evaluating a SIEM such as NewEvol against modern detection requirements can put the questions above to any vendor and ask for documented evidence of how detection performs when no predefined rule applies.
Conclusion: Expand Detection Beyond Known Patterns
Rule-based detection is valuable, but its logic reflects the threats and behaviours defenders have already anticipated. Attackers who change techniques, misuse trusted tools or chain ordinary actions into unusual sequences can operate in the space between rules.
A resilient strategy combines well-maintained rules with behavioural analysis, anomaly detection, contextual correlation and continuous testing. Judge detection breadth through practical evidence, especially what happens when a technique matches no existing rule.
Effective SIEM detection is not about replacing one approach with another. It is about combining complementary methods to improve visibility while keeping false positives and operational workload manageable.
Frequently Asked Questions
1. What are the main limitations of rule-based SIEM detection?
The main rule-based SIEM limitations come from the fact that rules only describe threats someone already understood. They can miss new techniques, modified versions of known attacks, misuse of legitimate tools and unusual event sequences. They also depend on the right telemetry being collected and on conditions broad enough to catch variations.
2. Why can rule-based SIEM systems miss zero-day attacks?
A zero-day exploits a weakness defenders do not yet know about, so no specific rule or signature exists for it. Rules may still catch related activity, such as unusual process launches or data movement after the exploit, but only if that later behaviour matches existing detection logic.
3. What is the difference between rule-based detection and anomaly detection?
Rule-based detection checks whether activity matches a predefined condition, such as ten failed logins in five minutes. Anomaly detection checks whether activity departs from an expected pattern. Rules are precise and explainable for known threats, while anomaly detection can surface unfamiliar activity but needs context to judge intent.
4. Can behavioural analytics detect threats without predefined rules?
Yes, within limits. Behavioural analytics compares activity against baselines of normal behaviour, so it can flag unusual actions that no rule describes. Its accuracy depends on data quality, reliable baselines and tuning, and its findings still need analyst investigation, because unusual activity is not always malicious.
5. Does anomaly detection eliminate false positives?
No. Anomaly detection often introduces false positives of its own, because legitimate changes such as new projects, seasonal workloads or system migrations can look unusual. Tuning, baseline maintenance, risk-based prioritization and added context reduce the noise, but some investigation effort always remains.
6. What should enterprises ask a SIEM vendor about unknown threat detection?
Ask how the platform would identify an attack technique that has no existing rule. A credible answer explains the detection mechanism, the telemetry it needs, its known limitations and how it has been validated. Be cautious of answers that rely only on broad references to AI or automation.