At 2:40 a.m., a finance server at a Riyadh head office starts sending data to an unfamiliar external address. By morning, the security team knows something happened, but not how. Firewall logs were kept for only a few days, the domain controller was never connected to the central console, and the server’s clock was eleven minutes off from every other system. The team has fragments, but it cannot rebuild the sequence or show an assessor what was detected, when, and by whom.
Logging and monitoring controls exist to close this gap. Centralized logging gives investigators one consistent record. Continuous monitoring turns that record into early warning. Together, they provide what compliance reviews expect: proof that security controls are operating, not just installed.
For organizations subject to the National Cybersecurity Authority’s Essential Cybersecurity Controls, this is a direct concern. Choosing a SIEM for NCA ECC readiness is less about features and more about evidence. This article explains what that evidence looks like and how to tell whether your environment can produce it.
Understanding NCA Essential Cybersecurity Controls (ECC)
The National Cybersecurity Authority (NCA) is Saudi Arabia’s national authority for cybersecurity. Its Essential Cybersecurity Controls set minimum cybersecurity requirements for organizations in scope. The ECC was first issued in 2018 and has since been updated, so confirm which edition applies to you.
The controls are organized into main domains covering cybersecurity governance, defense, resilience, and third-party and cloud computing security. The defense domain includes a subdomain dedicated to cybersecurity event logs and monitoring management, alongside related areas such as incident and threat management.
Applicability matters. The ECC applies to government organizations, their companies and entities, and private organizations that own, operate, or host Critical National Infrastructure. Sector regulators may add their own requirements, and other organizations often adopt the controls as good practice.
Two principles shape everything that follows. Technical controls must be mapped to the specific ECC requirements that apply to you, and the ECC expects documented policies, assigned responsibilities, and periodic review, not technology alone.
What Role Does SIEM Play in NCA ECC Compliance?
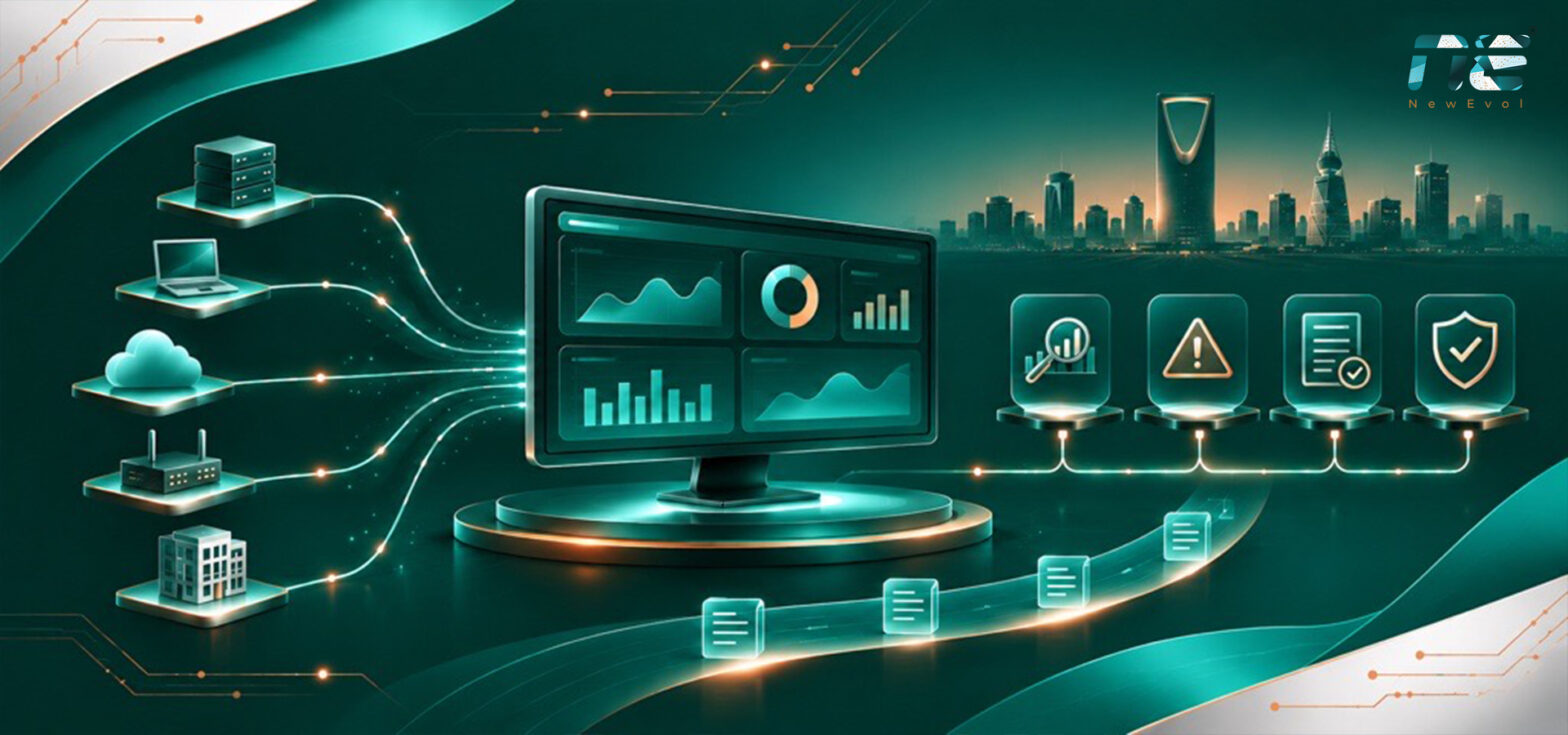
Security Information and Event Management (SIEM) brings security data into one place and makes it usable. In practice, a SIEM:
- Collects logs from servers, network devices, cloud services, and security tools
- Normalizes events into a consistent format and correlates related activity
- Identifies suspicious behavior and generates alerts for investigation
- Supports incident detection and response workflows
- Maintains searchable records of security events
- Produces reports that support compliance reviews
That last role is often underrated. A well-run SIEM shows that monitoring happens consistently: which sources reported, which alerts fired, and what analysts did about them.
A SIEM is still an enabling technology. It does not write your policies, staff your SOC, or decide who escalates an incident. Compliance depends on how the platform is configured, operated, and governed.
Critical Logging Sources Your SIEM Should Cover
Monitoring is only as good as the data behind it. Key sources include:
- Network devices: firewalls, routers, switches, VPN gateways, and network security appliances.
- Identity and access management: authentication events, failed logins, privileged account activity, and access changes.
- Endpoints and servers: operating system events, endpoint detection alerts, process activity, and system changes.
- Cloud environments: administrative actions, access events, and configuration changes.
- Business applications and databases: application access, sensitive data queries, and administrative operations.
- Security infrastructure: antivirus, EDR, IDS/IPS, and email security tools.
Not every system needs the same depth. Prioritize by business risk, system importance, and applicable controls. A core banking database deserves more detailed logging than a print server.
Watch for silent weaknesses: a source that stopped sending logs weeks ago, timestamps that disagree across systems, or events missing the user or source IP field. Any of these can break an investigation.
Log Retention, Integrity, and Evidence Management
Collected logs must also stay trustworthy and available. Good practice includes:
- Defining retention periods based on applicable controls, sector rules, and business needs
- Protecting logs from unauthorized modification or deletion
- Synchronizing time sources across all systems
- Restricting and recording access to log data
- Keeping historical records searchable, not just archived
- Documenting collection and retention procedures
Be careful with retention. The ECC addresses the retention of cybersecurity event logs, but take the required period from the current official control document and any sector-specific regulation that applies, not from vendor material or general guidance.
A simple test: can you state where logs are stored, who can access them, how long they are kept, and how their integrity is protected? If any answer is unclear, an assessor will notice.
Real-Time Monitoring and Threat Detection Capabilities
Continuous security monitoring aims to catch suspicious activity while it is still small. Useful detection focuses on authentication and access patterns, unusual privileged account activity, suspicious network connections, repeated failed logins, and abnormal data access or transfers, with alerts prioritized by severity and business impact.
Consider an example. An account records twelve failed logins within a few minutes. Shortly after, it logs in successfully from a country the employee has never worked from, then opens a restricted HR file share. Each event alone looks routine. Correlated across identity, VPN, and file server logs, the sequence points to a likely credential compromise.
Detection still needs people. Alerts require trained analysts, defined investigation steps, and escalation paths that work outside office hours. An alert nobody reviews provides neither protection nor evidence.
What Evidence Should Your SIEM Provide During an NCA ECC Assessment?
Dashboard screenshots rarely satisfy an assessor. What matters is showing that controls operate over time. The ECC requires logging and monitoring to be defined, implemented, and periodically reviewed; the checklist below is a recommended way to evidence that, not an official NCA list.
- Approved log management and monitoring policies
- An inventory of integrated log sources mapped to critical assets
- Collection-health reports showing logs arrive consistently
- Retention and access control configurations
- Time synchronization records
- Sample alerts with matching investigation records
- Documented incident escalation procedures
- Monitoring activity and operational reports
- Audit trails of access to sensitive log data
- Records of periodic review and control testing
- Named owners for monitoring and incident handling
- A register of identified gaps and corrective actions
Keep evidence dated, versioned, and linked to the relevant control. “Alerting is enabled” says little. “These alerts fired last quarter, and here is how each was handled” says a great deal.
Common SIEM and Logging Gaps That Can Create Compliance Problems
The same weaknesses appear across many organizations:
- Critical systems never connected to the SIEM
- Collection that breaks quietly after upgrades or migrations
- Retention policies that exist on paper but not in configuration
- Unsynchronized clocks
- Broad administrative access to log repositories
- Detection rules written once and never reviewed
- Alerts closed without investigation notes
- No clear owner for monitoring
- Escalations made by phone that leave no record
- No regular testing of detections
For example, an organization moves its email platform to the cloud but never connects the new audit logs. The dashboard looks healthy, yet suspicious mailbox activity is invisible. Periodic gap assessments find issues like this before an assessor, or an attacker, does.
How to Evaluate a SIEM Platform for NCA ECC Readiness
When assessing a SIEM for NCA ECC requirements, ask:
- Can it collect logs from all critical systems, including cloud and legacy platforms?
- Does it support centralized log management and event correlation?
- Can it detect suspicious activity across multiple data sources?
- Are historical records searchable across your required retention period?
- Can access to logs be controlled and audited?
- How does it demonstrate log integrity and retention?
- Does it support incident investigation and documentation?
- Can it generate monitoring reports and audit evidence?
- How does it flag missing sources or collection failures?
- Can detection rules be tested and reviewed?
- How does it integrate with incident response workflows?
- Which operational responsibilities remain with your team?
Ask vendors to demonstrate each point with realistic data. A general claim of compliance readiness is not evidence.
Building a Stronger SIEM Monitoring and Compliance Strategy
- Review applicable ECC requirements and identify the relevant logging and monitoring controls.
- Inventory critical systems and log sources.
- Define centralized logging and retention policies.
- Apply access controls and log integrity safeguards.
- Configure meaningful detection rules and event correlation.
- Assign monitoring ownership and escalation responsibilities.
- Maintain investigation and audit records.
- Test log coverage and detections periodically.
- Review effectiveness and close identified gaps.
Platforms such as NewEvol can support centralized security monitoring, event visibility, and evidence reporting within this approach. The platform provides visibility; the process around it determines whether controls hold up under review.
Conclusion: Prove Your Monitoring, Not Just Your SIEM Deployment
A SIEM contributes to compliance when it delivers reliable log visibility, meaningful threat detection, traceable investigations, and verifiable operational evidence. Technology, people, policies, and documentation all have to work together.
The practical test is straightforward. You should be able to show what is being logged, how suspicious activity is identified, who investigates alerts, and what evidence proves those controls are working.
Frequently Asked Questions
1. What is NCA ECC in Saudi Arabia?
The Essential Cybersecurity Controls are the National Cybersecurity Authority’s baseline cybersecurity requirements. They apply to government organizations, their companies and entities, and private operators of Critical National Infrastructure, covering governance, defense, resilience, and third-party and cloud security.
2. How does SIEM support NCA ECC compliance?
A SIEM centralizes logs, correlates events, and generates alerts, supporting the ECC’s monitoring and incident management expectations. It also keeps records and reports that help show controls are operating. It supports compliance but cannot achieve it alone.
3. What logs should organizations collect for NCA ECC readiness?
Start with critical assets: identity systems, firewalls and VPNs, servers and endpoints, cloud platforms, business applications, databases, and security tools. Prioritize by business risk and applicable controls, and make sure timestamps are consistent and event fields complete.
4. Does NCA ECC specify log retention requirements?
Yes, the ECC addresses retention of cybersecurity event logs. Take the exact period from the current official NCA control document, and check sector-specific regulations that may add requirements. Then confirm your SIEM configuration actually matches the documented policy.
5. What SIEM evidence may be required during an NCA ECC assessment?
Common evidence includes approved policies, a log source inventory, collection-health records, retention and access settings, time synchronization records, sample alerts with investigation notes, escalation procedures, review records, and a register of gaps and corrective actions.
6. Why is continuous security monitoring important for compliance?
It shows that detection happens consistently, not occasionally. Continuous monitoring shortens the time between suspicious activity and response, and it builds an ongoing record that demonstrates control effectiveness during internal reviews and external assessments.
7. Can deploying a SIEM platform guarantee NCA ECC compliance?
No. A SIEM is a tool. Compliance also depends on documented policies, correct configuration, trained staff, defined escalation, and evidence of periodic review. A poorly integrated or unattended SIEM can leave significant control gaps.
8. How can organizations identify gaps in their SIEM logging and monitoring?
Run periodic gap assessments. Compare log sources against critical assets, review collection-health reports, test detection rules with simulated activity, check closed alerts for investigation notes, and confirm retention and access settings match policy.